Information Security Policy
Information security policy
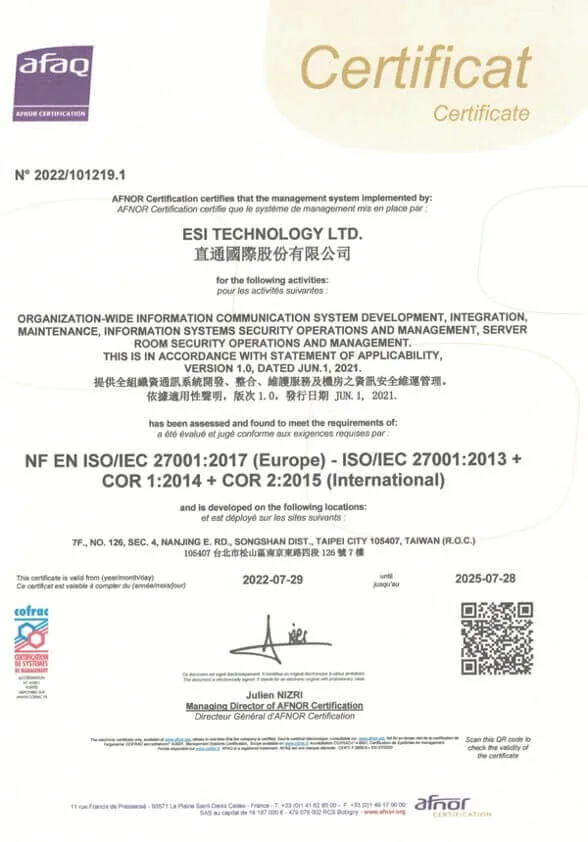
An information security management system certified to ISO/IEC 27001
We protect the confidentiality, integrity and availability of our information assets and comply with relevant regulations, so clients can entrust their data to us with confidence.
I. Purpose
ESi Technology Ltd. (hereinafter the "Company") maintains the confidentiality, integrity and availability of its information assets, complies with the requirements of relevant laws and regulations, and safeguards users' data privacy, protecting them from intentional or accidental internal and external threats. The Company has integrated the information security objectives of its departments at every level and established the following overall information security policy objectives:
Information security policy objectives
Four objectives
-
Confidentiality
Protect information on the Company's business activities from unauthorized access to ensure confidentiality.
-
Integrity
Protect information on the Company's business activities from unauthorized modification to ensure accuracy and integrity.
-
Availability
Establish an information business continuity plan to keep the Company's business operating and ensure availability.
-
Regulatory compliance
Ensure the Company's business is conducted in line with the requirements of relevant laws and regulations to ensure regulatory compliance.
II. Scope
This policy applies to, and shall be complied with by, the Company's personnel, outsourced service providers and visitors, together with the management of the related information and communication security operating rules. Its aim is to prevent improper use, leakage, alteration, destruction or similar incidents involving data caused by human error, intentional acts, natural disasters or other factors, which could expose the Company to various risks and harm. In addition to the "Statement of Applicability", "Document Management Procedure", "Management Review Procedure", "Information Security Audit Management Procedure" and "Corrective and Preventive Action Management Procedure", information and communication security management follows the procedures below:
- Establishing and evaluating the information security policy (Information Security Policy, Information Security Objectives Management Procedure, Organizational Context Analysis Procedure).
- Information security organization (Information Security Organization Management Procedure).
- Personnel information security management and training (Human Resources Security Management Procedure).
- Classification and control of important information assets (Information Asset Management Procedure).
- Risk identification and control (Information Security Risk Management Procedure).
- Access control security (Access Control and Password Management Procedure).
- Physical and environmental security (Physical and Environmental Security Management Procedure).
- Operations security management (Operations Security Management Procedure).
- Network security management (Network Security Management Procedure).
- Security in the acquisition, development and maintenance of information systems (System Development and Maintenance Management Procedure).
- Supplier service management (Supplier Relationship Management Procedure).
- Response to and handling of information security incidents (Information Security Incident Management Procedure).
- Business continuity management (Business Continuity Management Procedure).
- Compliance with relevant laws and regulations and Company policies (Regulatory Compliance Management Procedure)
III. Responsibilities
Responsibilities for implementing the security policy
Information Security Committee
The Company has an Information Security Committee. The co-founders nominate one of themselves as an ex officio member and Chief Information Security Officer (CISO). The committee oversees coordination and management review of security policies, plans, operations and resource allocation.
Information Security Working Group
An Information Security Working Group sits under the committee. The CISO designates a management representative to draft and revise procedures at all levels as security needs require and keep the ISMS effective. Work results are reported to the committee for management review at least once a year.
All units
All units of the Company shall follow the information security rules established by the Information Security Working Group.
Employees, remote users and vendors
The Company's employees, users connecting to its systems from outside its offices, and vendors undertaking business for the Company shall follow the Company's information security policy and related management rules.
Liability for violations
Anyone who engages in any conduct that endangers information security shall bear civil and criminal liability in accordance with the law and be subject to administrative discipline under the Company's relevant rules.
ISO/IEC 27001
ISO 27001 certified in 2022
ESi implemented an information security management system (ISMS) in 2021 and achieved ISO 27001:2013 certification in June 2022, covering system development, system integration, maintenance services and data center security operations. Before software projects are delivered to clients, they are also security tested and remediated with Fortify.
Last edited: 2022.06.03
Questions about our security management?
Contact us, and we'll explain our information security management system and related practices.